Dunning in Spam? Recover Subscription Payments Sep 2026
Dunning emails flagged as spam cause considerable revenue loss, with 20-40% of total customer churn. When payment reminders never reach customers' inboxes, failed transactions escalate into cancelled subscriptions. Modern recovery platforms using AI-powered retry logic, proper email authentication protocols, and omnichannel messaging can achieve 2-4x better recovery rates.
At a Glance
• Failed payment recovery emails land in spam for nearly half of senders, with 48% cite spam avoidance as top challenge
• Implementing SPF, DKIM, DMARC and BIMI authentication protocols is now mandatory for bulk senders under Gmail and Yahoo's 2024 requirements
• AI-powered retry systems that decouple payment attempts from email notifications achieve 42% average recovery rates versus static retry schedules
• SMS messaging delivers 98% vs 20% open rate, making omnichannel approaches necessary for payment recovery
• Pre-dunning emails sent before card expiration show higher success rates than post-failure dunning messages
• GDPR permits dunning emails under legitimate interest provisions without explicit consent when used transparently for payment recovery
Missed cash hides in your spam folder. When dunning emails never reach customers, payment failures snowball into churn. This post shows how to harden your tech stack and messaging so dunning emails land, get read, and trigger successful retries.
Why spam-boxed dunning emails drain revenue
When dunning emails land in spam, customers never see the payment reminder, and what could have been a quick card update turns into a cancelled subscription. Involuntary churn, the kind caused by payment failures instead of customer choice, accounts for 20-40% of total customer churn. Across the subscription economy, Churnkey's 2025 analysis of over $3 billion in subscription revenue tracked 6 million failed payments, which shows how widespread the problem is.
Deliverability itself is a major pain point: 48% of senders struggle with spam. Every dunning email that disappears into junk folders represents lost MRR, higher support costs, and customers who churn without ever knowing their card failed.
Key takeaway: Deliverability is not a marketing problem; it is a revenue problem. Fix it before you lose subscribers who wanted to stay.
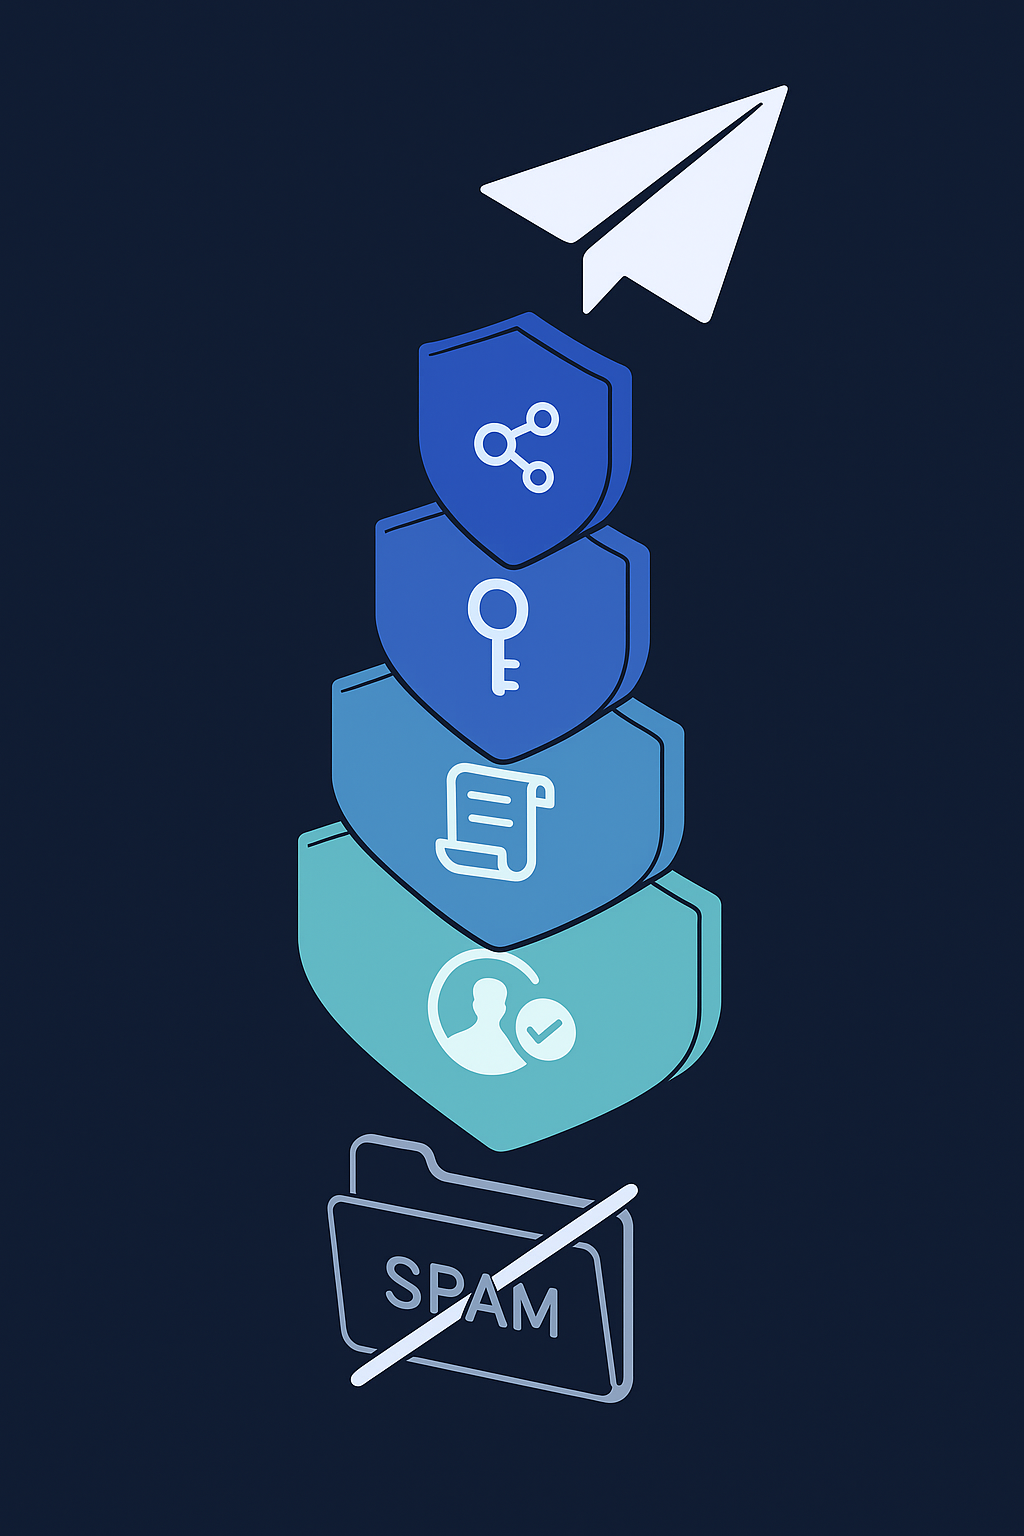
How do SPF, DKIM, DMARC & BIMI keep dunning emails out of spam?
Email authentication is a layered defence that proves your messages are legitimate. Here is what each protocol does and how to set it up:
Protocol | What it does | Setup essentials |
|---|---|---|
SPF | Specifies which IP ranges may send on behalf of your domain | Publish a DNS TXT record listing authorised senders; end with |
DKIM | Adds a cryptographic signature so receivers can verify the message came from your domain | Generate a key pair, publish the public key in DNS, sign outbound mail |
DMARC | Tells receivers how to handle messages that fail SPF or DKIM, and sends you reports | Publish a DNS TXT record with policy ( |
BIMI | Displays a verified logo in the inbox when DMARC is enforced | Requires enforced DMARC, a trademarked logo in SVG format, and a Verified Mark Certificate |
Bulk senders must use SPF and DKIM to comply with Gmail and Yahoo's bulk sender requirements (introduced in 2024 and since tightened). Google now asks senders to keep spam complaint rates under 0.1% complaint rate threshold.
DKIM alignment matters too. DKIM lets organisations claim message responsibility. Aligning the "From" domain with the DKIM signature closes the loophole spoofers exploit, and sending from your own authenticated domain instead of a vendor's shared domain is equally important for inbox placement.
Key takeaway: Implement all four protocols, monitor DMARC reports, and rotate DKIM keys regularly to maintain inbox placement.
What message tactics stop ISPs flagging your dunning emails?
Even with perfect authentication, poorly crafted messages can trigger spam filters or annoy customers into clicking "Report spam." Use these tactics to lift opens and reduce complaints:
- Send the first email immediately. An analysis of over 1 million dunning emails found that emails sent on the day of failure have the highest open and recovery rates, with subsequent emails still contributing meaningful revenue when the cadence extends to 30 days, according to Baremetrics.
- Personalise and keep a cheerful tone. 62% prefer personalised over generic messages. Use the customer's name, reference their plan, and avoid alarmist language.
- Tap into loss aversion. Emphasise what the customer will lose (access to saved data, premium features) instead of what you need from them. Loss aversion is a powerful psychological driver.
- Use pre-dunning emails. Baremetrics found that pre-dunning emails, sent before a card expires, outperform post-failure dunning emails.
- Keep list hygiene tight. Remove hard bounces immediately, suppress unengaged contacts, and monitor blocklists.
Key takeaway: Combine timely, personalised messaging with proactive pre-dunning to maximise recovery while keeping complaint rates low.
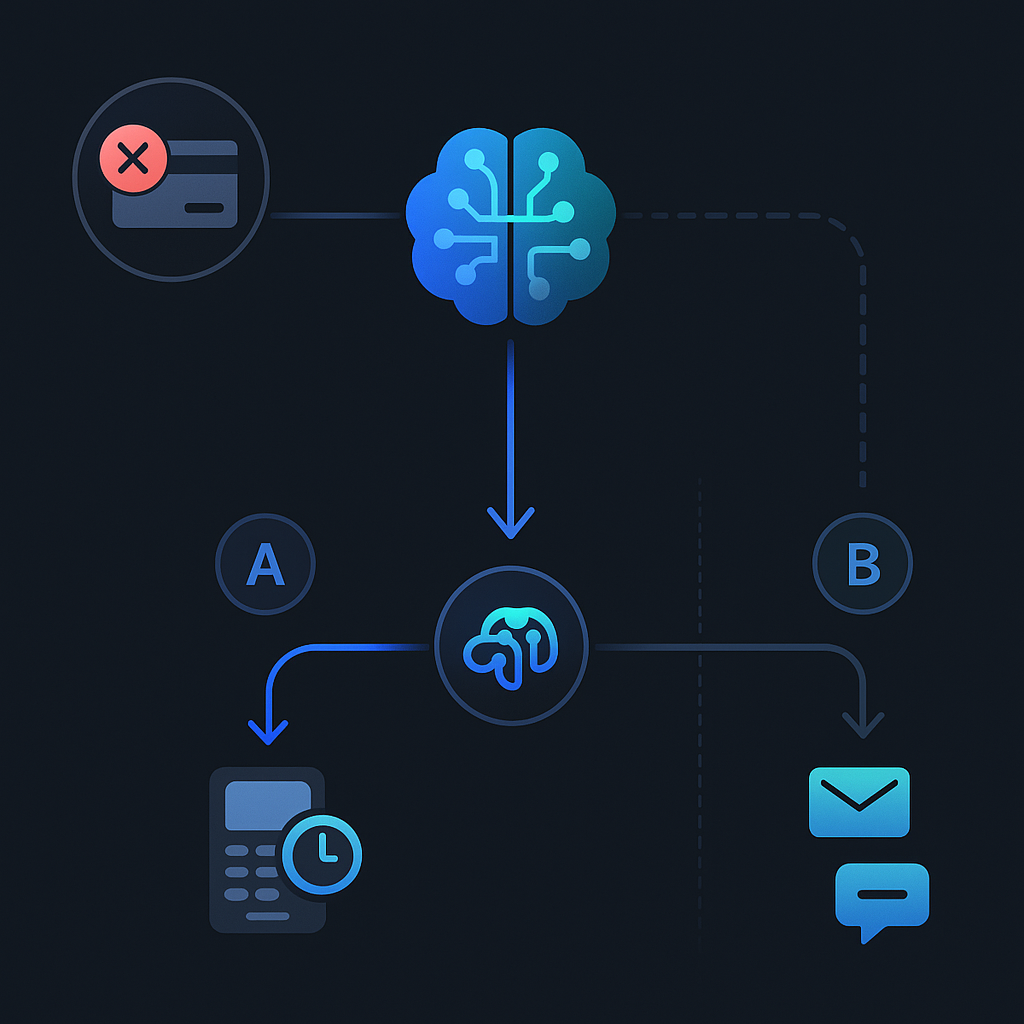
Decouple payment retries from emails with AI smart logic
Sending an email after every failed retry is a recipe for dunning email fatigue and spam complaints. Modern recovery stacks separate retry logic from messaging entirely (AI vs rules-based recovery), letting AI decide when to charge the card and when to nudge the customer.
Recurly's Intelligent Retries, for example, uses AI to optimise retry timing. The system analyses billions of transactions to find patterns that improve success rates without spamming the inbox.
Stripe's Smart Retries takes a similar approach, recovering $9 recovered per $1 spent on Billing. The key insight is that the best time to retry many failed payments is often days into the future, not minutes.
Stripe's Smart Retries takes a similar approach, recovering $9 recovered per $1 spent on Billing. The key insight is that the best time to retry many failed payments is often days into the future, not minutes.
The system's AI engine claims 2-4× better recoveries than static retry systems, assessing issuer behaviour, day-part, and historical patterns to schedule each retry individually.
Key takeaway: Decouple retries from emails, let AI pick retry timing, and reserve customer outreach for when it truly matters.
Which omnichannel nudges recover payments faster than email?
Email is not the only, or even the best, channel for payment recovery. SMS, in-app messaging, and paywalls bypass the inbox entirely and reach customers where they are already engaged.
- SMS: Churnkey reports that SMS 98% vs email 20% open rate. A short, well-timed text can prompt immediate action.
- In-app payment walls: Restricting access to premium features until the customer updates their card keeps the reminder front and centre. Churnkey notes that in-app payment walls can improve recovery rates per Churnkey.
- Planning prompts: Research published in the Journal of Consumer Psychology found that adding a minimalist planning prompt, asking customers to specify when they will pay, lifted delinquency cure rate by 2.26 points. These prompts are virtually free to implement.
Key takeaway: Layer SMS and in-app nudges on top of email to capture customers who never check their inbox.
Stay lawful: GDPR, legitimate interest & transactional email
Dunning emails are transactional, not promotional, but that does not give you carte blanche under GDPR. Here is how to stay compliant:
- Legitimate interest applies. The European Data Protection Board's guidelines confirm that direct marketing qualifies as legitimate interest. Payment reminders that help customers avoid service interruption typically qualify.
- Consent is not always required. Infobip explains that GDPR consent not required for transactional emails.
- Penalties are steep. The GDPR authorises regulators to levy fines of up to €20 million or 4% of revenue.
Best practices:
- Document your legitimate-interest assessment.
- Limit data collection to what is necessary for payment recovery.
- Provide a clear way for customers to update preferences or delete data.
- Avoid adding promotional content to dunning emails; keep them purely transactional.
Key takeaway: Transactional emails enjoy more flexibility under GDPR, but sloppy practices can still attract enforcement.
Churn Buster alternatives for AI-powered dunning and payment retries in 2026
Churn Buster is a well-known dunning tool, but the market has evolved well beyond rule-based email sequences. If you are assessing alternatives, or outgrowing what Churn Buster's static retry logic can do, here is how the current market stacks up.
Tool | Core approach | Key limitation |
|---|---|---|
Churn Buster | Configurable email/SMS dunning sequences; integrates with Stripe and Braintree | Retry timing is rule-based, not AI-driven; limited to gateways it directly integrates with |
ProfitWell Retain | Dunning automation bundled within the ProfitWell (Paddle) analytics suite | Tightly coupled to Paddle's billing ecosystem; limited multi-gateway flexibility |
Stripe Billing Smart Retries | ML-driven retry timing within the Stripe network | Only works for Stripe-processed payments; no cross-gateway intelligence |
Slicker | Artificial Payments Intelligence sits on top of existing billing infrastructure; multi-gateway routing; pay-for-success pricing | Best suited for higher-volume subscription businesses; lighter value at very low MRR |
The critical differentiator between Churn Buster and newer AI-first platforms is where intelligence sits. Churn Buster optimises the message sequence: when to email, what to say. Slicker's Artificial Payments Intelligence optimises the retry itself: which gateway to route through, what time of day, what day of the billing cycle, based on issuer-level and card-type behavioural patterns. Importantly, Slicker's AABB testing with statistical significance lets you measure this uplift on your own traffic before committing, giving you verified proof over vendor assurances. These are complementary problems, but the retry layer typically recovers more revenue than the messaging layer alone, because many soft declines never need a customer email at all: they resolve on a well-timed silent retry.
For businesses processing payments across multiple gateways or geographies, a system that operates across the full stack (retry intelligence plus omnichannel dunning plus multi-gateway routing) will consistently outperform tools scoped to a single gateway or a single channel.
Key takeaway: If Churn Buster's rule-based sequences are your entire recovery stack, you are likely leaving the largest recovery opportunity (smart retry timing) untouched. Assess tools that decouple retry logic from messaging, validate uplift via AABB testing on your own data, and operate across your full gateway estate.
Slicker vs billing-native recovery: what's the smarter choice?
Billing platforms like Stripe, Recurly, and Zuora include basic retry logic, but they optimise primarily within their own gateways. Slicker takes a different approach, sitting on top of existing billing and payment systems to provide cross-platform intelligence. Where billing-native retries rely on fixed schedules or single-gateway logic, Slicker's AI assesses issuer behaviour, day-part, and historical patterns per transaction, then routes each attempt through the gateway with the highest predicted approval rate. Slicker proves that uplift via AABB testing with statistical significance on your own traffic before you commit. The result is transparent, unified analytics across all gateways, a five-minute no-code setup, and pay-for-success pricing where you only pay for payments actually recovered (Slicker's pilot runs for four months: the first month is a free trial, followed by three paid months, with the option to cancel anytime).
The system prioritises intelligent retry timing, multi-gateway routing, and transparent analytics, whereas most competitors optimise mainly within one gateway. Performance is validated through AABB testing on each customer's own traffic, not through vendor-reported benchmarks.
For context, Stripe's Adaptive Acceptance recovered $6 billion in falsely declined transactions, but that capability is locked to Stripe-processed payments.
Pay-for-success vs SaaS fees
Traditional SaaS pricing models charge monthly fees regardless of performance. Pay-for-success aligns vendor and customer incentives, reducing risk for businesses adopting AI retry solutions. You pay only when revenue is actually recovered.
Key takeaway: If your billing provider's native retries are underperforming, an overlay solution can unlock incremental recovery without ripping out your stack.
How to handle failed ACH and direct debit payments differently from card failures
Card declines and ACH/direct debit failures are not the same problem, and treating them identically costs you recoverable revenue. The mechanics, retry rules, and customer communication each diverge considerably.
How this plays out in practice: For card failures, let AI retry logic exhaust recoverable soft declines before sending a customer-facing email. For ACH returns governed by NACHA (the US ACH network rules body), especially authorisation-revoked codes (R07, R10), send a customer notification immediately, because the bank won't let you retry and only the customer can re-authorise the mandate. A single dunning sequence that treats both failure types identically will either over-message card customers or under-message ACH customers who genuinely need to act. Building a failure-reason dunning cadence that routes each decline code to the right recovery track is the practical fix.
Account updater services (Visa, Mastercard, and Amex all offer these, and Stripe, Adyen, and Braintree expose them via their APIs) automatically refresh stored card credentials when a card is reissued, eliminating a large share of card-failure dunning entirely. No equivalent exists for bank accounts, since ACH credential refresh is always a manual customer action.
Key takeaway: Build two distinct recovery tracks: an AI-optimised retry track for card soft declines, and a high-urgency customer-action track for ACH/direct debit returns, particularly for mandate-revocation codes where retry is prohibited.
KPIs to track after you fix deliverability
Once your dunning emails land and your retry logic is optimised, measure success with these metrics:
- Involuntary churn rate: The percentage of customers who leave due to payment failure, not an active cancellation. Churnkey's data shows voluntary ~7% vs involuntary ~1% churn. If your involuntary rate is higher, there is room to improve.
- Recovery rate: The percentage of failed payments that are eventually collected. The average recovery rate was 42% through dunning emails and SMS campaigns in Churnkey's analysis.
- Dunning email performance by day: Track open rate, click rate, and recovery rate for each email in the sequence. Baremetrics data shows day-zero emails achieve 41.29% open rate and 13.25% recovery rate, while day-30 emails still contribute.
- Previous-payment success as a predictor: Propensity-to-pay models find that 95% on-time when prior invoice paid. Use this signal to segment high-risk accounts for proactive outreach.
Key takeaway: Track these KPIs weekly, A/B test email copy and retry timing, and feed learnings back into your dunning strategy.
What's changed in 2026: the authentication crisis raises the stakes
Email deliverability rules have tightened considerably since early 2025. What was once a reputation-based system (where suspicious mail landed in spam and bounced) has become a binary pass-or-fail model. According to a 2026 analysis by Mailbird, Gmail, Yahoo, and Microsoft now enforce SPF, DKIM, and DMARC compliance simultaneously with full alignment, and organisations that fall short face complete delivery failure, beyond spam folder placement alone.
This matters acutely for dunning emails. A payment reminder that hard-bounces never reaches the customer at all, turning a recoverable soft decline into silent involuntary churn. Even fully authenticated senders face new pressure: unspam.email's 2025 analysis found spam placement rates above 30% for mail that passes all three authentication checks, underlining that engagement signals, such as open rates, deletion rates, and complaint rates, now carry as much weight as the protocols themselves.
On the recovery side, Baremetrics' 2026 subscription payment benchmarks show a median attempted recovery rate of 12.7% across its sample: a useful baseline against which to measure your own dunning programme. Businesses using AI-powered retry logic consistently outperform that median; recovery rates vary by subscriber mix and billing infrastructure, so your own historical baseline is the most reliable reference point for gauging improvement.
Key takeaway: In 2026, authentication is the price of entry, not a competitive advantage. Audit your SPF, DKIM, and DMARC alignment now, and track engagement metrics as closely as you track delivery rates, because inbox providers are doing the same.
Key takeaways: recovery without the spam risk
Recovering failed subscription payments does not have to mean flooding inboxes or fighting spam filters. Here is the playbook:
- Authenticate your domain with SPF, DKIM, and DMARC. Aim for a DMARC policy of
p=rejectto prevent spoofing. - Keep complaint rates low by personalising dunning emails, using a friendly tone, and extending the cadence to 30 days.
- Decouple retries from emails. Let AI choose the best retry window; reserve customer outreach for moments that matter.
- Go omnichannel. SMS and in-app walls reach customers who never open email.
- Stay GDPR-compliant. Document legitimate interest, keep messages transactional, and respect data-subject rights.
- Measure and iterate. Track involuntary churn rate, recovery rate, and per-email performance.
Slicker's AI-powered system reshapes the way businesses handle failed subscription payments. It connects directly with existing payment rails and processes to reduce involuntary churn, increase recovered revenue, and boost business margins. If your current setup is leaving money in spam folders, intelligent retries can make a measurable difference.
Frequently Asked Questions
What are dunning emails and why are they important?
Dunning emails are payment reminders sent to customers when a subscription payment fails. They are key for recovering failed payments and reducing involuntary churn, which can account for 20-40% of total customer churn.
How can I prevent dunning emails from being marked as spam?
To prevent dunning emails from being marked as spam, implement email authentication protocols like SPF, DKIM, DMARC, and BIMI. These protocols help verify the legitimacy of your emails and improve deliverability.
What are some effective strategies for improving dunning email performance?
Effective strategies include sending the first email immediately after a payment failure, personalizing messages, using a friendly tone, using loss aversion, and adding pre-dunning emails to remind customers before their payment method expires.
How does AI improve payment recovery for failed subscriptions?
AI improves payment recovery by decoupling retry logic from emails, allowing machine learning to determine the optimal time for retrying payments. This approach reduces customer fatigue and increases recovery rates by analyzing transaction patterns.
What are the benefits of using omnichannel nudges for payment recovery?
Omnichannel nudges, such as SMS and in-app messaging, bypass email and reach customers directly. These channels have higher engagement rates, with SMS boasting a 98% open rate, and can markedly improve payment recovery rates.
How does Slicker enhance payment recovery compared to billing-native solutions?
Slicker enhances payment recovery by using AI to optimize retry timing, applying multi-gateway routing, and providing transparent analytics. This approach consistently outperforms static retry systems, with uplift validated through clinical-grade AABB testing on each customer's own traffic, connecting directly with existing payment processes.
What PII does Slicker need to send dunning emails, and does GDPR data minimisation allow this?
Slicker accesses the minimum data needed to identify the customer and personalise a payment reminder: name, email contact, subscription plan, and the payment failure reason code. No full card numbers, bank account details, or unrelated personal data are required or stored. Under GDPR's data minimisation principle (Article 5(1)(c)), processing is lawful as long as data is "adequate, relevant and limited to what is necessary" for the stated purpose. Recovering a specific failed payment is a clearly scoped purpose. Slicker's processing is grounded in legitimate interest (Article 6(1)(f)) instead of explicit consent, which means you do not need to re-obtain opt-in from customers before sending a dunning email. To stay compliant, document your legitimate-interest assessment, confirm your data-processing agreement with Slicker covers the categories above, and verify customers can request deletion of their data after the recovery window closes.
How does Slicker tailor dunning email messaging for different decline reasons, including sensitive ones like suspected fraud?
Slicker maps each decline code to a message variant that gives the customer enough context to act without exposing restricted or harmful information. For routine soft declines (insufficient funds, expired card), the email names the issue directly and provides a clear update-card CTA. For sensitive codes, particularly suspected fraud flags (e.g. Visa decline code 59, Mastercard code 63), the message is deliberately generic: it notifies the customer that their payment could not be processed and asks them to contact their bank or update their payment method, without stating that fraud was the trigger. This matters for two reasons: card network rules prohibit merchants from disclosing fraud-related decline reasons to cardholders, and surfacing a fraud flag can cause customer distress or prompt disputes. The result is a message that is actionable for the customer and compliant with network rules, while keeping your sender reputation intact.
What technical setup is required to send dunning emails from my own domain, and can I manage this without engineering?
Sending dunning emails from your own domain requires three DNS records (SPF, DKIM, and DMARC), which your Slicker onboarding guide walks through step by step. In practice this is a one-time, 15-30 minute task performed in your DNS provider's dashboard; no code is written. Once DNS propagates, Slicker routes outbound dunning emails through your authenticated domain so messages arrive from your brand, not a generic sender identity, which lifts deliverability and open rates. Beyond initial DNS setup, all dunning sequence configuration (timing, copy, cadence, channel mix) is managed through Slicker's no-code dashboard. Engineering involvement is not required to launch, adjust, or pause campaigns. Changes take effect without a deployment cycle.
How does Slicker integrate with Stripe technically, and what level of API access is required?
Slicker connects to Stripe via OAuth, which means you grant access through Stripe's standard permissions flow instead of sharing raw API keys. The permission scope is narrow by design: Slicker requests read access to subscription and payment data, and write access limited to the specific actions needed for recovery, such as retrying a charge, resetting a billing cycle anchor, or updating a subscription status. It does not request access to unrelated objects (payouts, Connect accounts, Radar rules). All actions Slicker takes, including retries, billing cycle resets, and subscription changes, are written back into Stripe as the system of record: they appear in your Stripe dashboard event log with a clear audit trail, so your finance and engineering teams can see exactly what happened and when. Slicker does not maintain a parallel subscription state; Stripe remains the single source of truth.
How does delta-based (incremental recovery) pricing work, and why is it fairer than a flat percentage of recoveries?
Most payment recovery tools charge a percentage of every payment they process, including ones your existing setup would have recovered anyway. Delta-based pricing charges only on the incremental uplift: the additional revenue Slicker recovers above your baseline. Here is why that distinction matters. If your current retry logic already recovers 30% of failed payments and Slicker lifts that to 50%, a flat-percentage model bills you on the full 50%. A delta model bills you only on the 20-point improvement, the revenue you genuinely would not have collected otherwise. Slicker measures this baseline through its clinical AABB testing methodology: traffic is split between your existing recovery stack and Slicker, recovery rates are measured with statistical significance, and the delta is the only thing billed. Vendors' incentives align with yours: Slicker is only paid when it outperforms what you already have, not when it processes recoveries you were going to collect regardless.
How can I monitor invoice recovery performance in Slicker after changing a dunning window?
After a dunning window change, Slicker's analytics dashboard surfaces recovery rate by cohort, segmented by the date the change took effect, so you can compare pre-change and post-change performance on an apples-to-apples basis without waiting for a full billing cycle. Beyond the AABB test dashboard, visibility tools include: per-email performance breakdowns (open rate, click rate, and recovery rate for each message in the sequence), decline-code-level recovery reports (so you can see whether a window change helped more for soft declines than hard ones), and a real-time payment event log that shows every retry attempt, its outcome, and which dunning email, if any, preceded the successful payment. For teams that want to pipe this data into their own BI stack, Slicker exposes a webhooks feed and a read API so recovery metrics can be joined with MRR, cohort, and LTV data in your existing reporting environment.
What are the best practices for dunning emails that actually get customers to update their payment info?
The highest-converting dunning emails share six characteristics: (1) Send immediately. Day-zero emails achieve the highest open and recovery rates; every day of delay lowers the odds the customer acts. (2) Use the customer's name and reference their specific plan. Personalisation lifts response rates and signals the email is legitimate, not a phishing attempt. (3) Lead with what they will lose, not what you need. Loss aversion is more motivating than a generic "please update your card." Mention the specific features or data at risk. (4) Include a single, standout CTA. Give a direct link to the payment update page, not a link to your homepage. Friction kills conversions. (5) Keep the tone calm and helpful, not threatening. Alarmist language increases spam complaints and damages sender reputation. (6) Send a pre-dunning email before the card expires. Proactive reminders before failure outperform reactive dunning after failure. Combine these tactics with proper SPF/DKIM/DMARC authentication so the email actually lands in the inbox, and decouple your retry logic so the customer is only emailed when a human action is genuinely needed, not after every automatic retry attempt.
What is the best way to reduce involuntary churn for a SaaS subscription business in 2026?
In 2026, the highest-impact involuntary churn reduction stack combines four layers: (1) Network tokenisation and account updater. Visa, Mastercard, Amex, and major gateways (Stripe, Adyen, Braintree) offer account updater services that automatically refresh stored card credentials when a card is reissued or a number changes, eliminating a large share of avoidable card failures before they ever reach dunning. (2) AI-powered retry timing. Machine learning models that assess issuer behaviour, day-part, and historical transaction patterns schedule each retry at the moment of peak approval probability, recovering soft declines silently without customer contact. (3) Omnichannel dunning. For failures that cannot be resolved by retry alone, layering SMS and in-app payment walls on top of email reaches customers who never open their inbox. (4) Visa and Mastercard retry compliance. Both networks now enforce retry limits and can levy fines for excessive retry attempts on hard-decline codes; a system that respects network rules avoids penalties while preserving your merchant standing. Businesses that implement all four layers consistently report involuntary churn rates near 1% of total subscriber base, compared to 3 to 5% for those relying on email-only dunning with static retry schedules.
Does Stripe Smart Retries recover as much revenue as a dedicated payment recovery service?
Stripe Smart Retries is effective within the Stripe network. The service reported recovering $9 in revenue for every $1 spent on Billing, but it operates exclusively on Stripe-processed payments and cannot route to alternative gateways when Stripe's approval rate on a given issuer is low. A dedicated payment recovery service like Slicker sits above the gateway layer, applying AI retry logic across multiple processors and routing each attempt through the gateway with the highest predicted approval rate for that specific card, issuer, and transaction type. For businesses processing all payments through Stripe, Smart Retries provides meaningful uplift at no additional cost. For businesses operating multiple gateways, processing internationally, or whose Stripe recovery rates have plateaued, a cross-gateway AI layer typically recovers incremental revenue that gateway-native logic cannot reach, because the optimisation space is wider than any single processor's model can see.
Sources
- https://www.slickerhq.com/blog/what-is-involuntary-churn-and-why-it-matters
- https://www.slickerhq.com/blog/comparative-analysis-of-ai-payment-error-resolution-slicker-vs-competitors
- https://www.mailgun.com/wp-content/uploads/pdf/SI-State_of_Email-2024_-_v3_1.pdf
- https://churnkey.co/reports/state-of-retention-2025
- https://churnkey.co/feature/payment-recovery/dunning-campaigns
- https://www.mailgun.com/resources/research/email-authentication-requirements/
- https://www.spamresource.com/2025/04/2025-magy-sender-compliance-guide.html
- https://m3aawg.org/sites/default/files/m3aawg-email-authentication-recommended-best-practices-09-2020.pdf
- https://baremetrics.com/blog/improve-dunning-recovery-rate
- https://docs.recurly.com/docs/retry-logic
- https://stripe.com/blog/how-we-built-it-smart-retries
- https://myscp.onlinelibrary.wiley.com/doi/full/10.1002/jcpy.1031
- https://www.edpb.europa.eu/system/files/2024-10/edpb_guidelines_202401_legitimateinterest_en.pdf
- https://infobip.com/blog/transactional-email-gdpr
- https://us.nttdata-solutions.com/hubfs/IB-C4HANA/IndustryGuide-SAP-Addressing-GDPR-Requirements-for-Customer-Data-Management.pdf
- https://stripe.com/blog/ai-enhancements-to-adaptive-acceptance
- https://www.slickerhq.com/blog/top-7-ai-retry-engines-2025-yc-backed-slicker-flexpay-gocardless
- https://pubsonline.informs.org/do/10.1287/LYTX.2024.03.06/full/
- https://www.slickerhq.com/contact
Related Articles
Build vs Buy: Payment Retry Logic Deep Dive (September 2026)
Your engineering team can build retry logic. The harder question is whether they should. The gap between a basic retry schedule and something that actually...
Where 20% More Payment Recovery Comes From (Sep 2026)
A 20% recovery uplift sounds like a headline until you try to figure out what it actually means for your baseline. Relative improvement, absolute percentage...
2026 Revenue Recovery Playbook for Subscription Businesses
Failed payments are responsible for somewhere between 20 and 40% of subscription churn across the industry. Those subscribers never chose to leave. A good...
Stop losing revenue to failed payments
Join leading subscription businesses using Slicker to recover failed payments automatically.
Get Started